Important
All writeups will be password-protected using the challenge flag, in accordance with HTB’s Terms of Service.
Update log
| Date | Writeup | Difficulty | |
|---|---|---|---|
| 2026-10-09 | JerryTok | Medium | |
| 2026-08-10 | SocratesPanel | Hard | |
| 2025-11-06 | Why Lambda | Hard | |
| 2025-10-31 | TornadoService | Medium | |
| 2025-10-26 | Interstellar | Medium | |
| 2025-10-24 | DoxPit | Medium | |
| 2025-10-22 | ScreenCrack | Medium | |
| 2025-10-20 | POP Restaurant | Easy |
In the next few weeks, I’ll be joining ASEAN Cyber Shield 2025 in Korea, once again taking on the role of a web exploiter. It’s the perfect excuse to refresh my skills and get back into the groove. Ever since I moved into a GRC role, I’ve noticed my hands-on skills have dropped more than I’d like to admit, so it’s definitely time to train again.
Whenever I need to focus on a specific area, Hack The Box is always my go-to playground. It’s where I revisit old techniques, explore new vulnerabilities, and challenge myself with realistic scenarios. This writeup is part of that preparation, capturing my approach, thoughts, and key takeaways along the way.
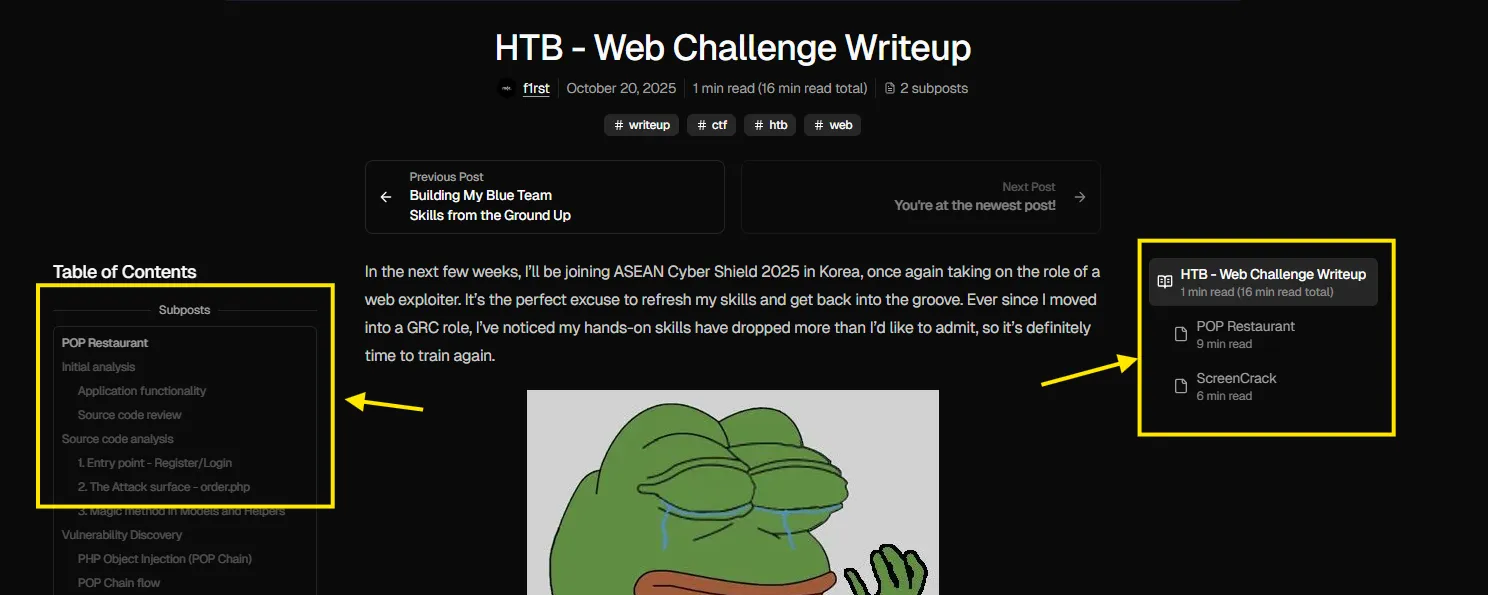
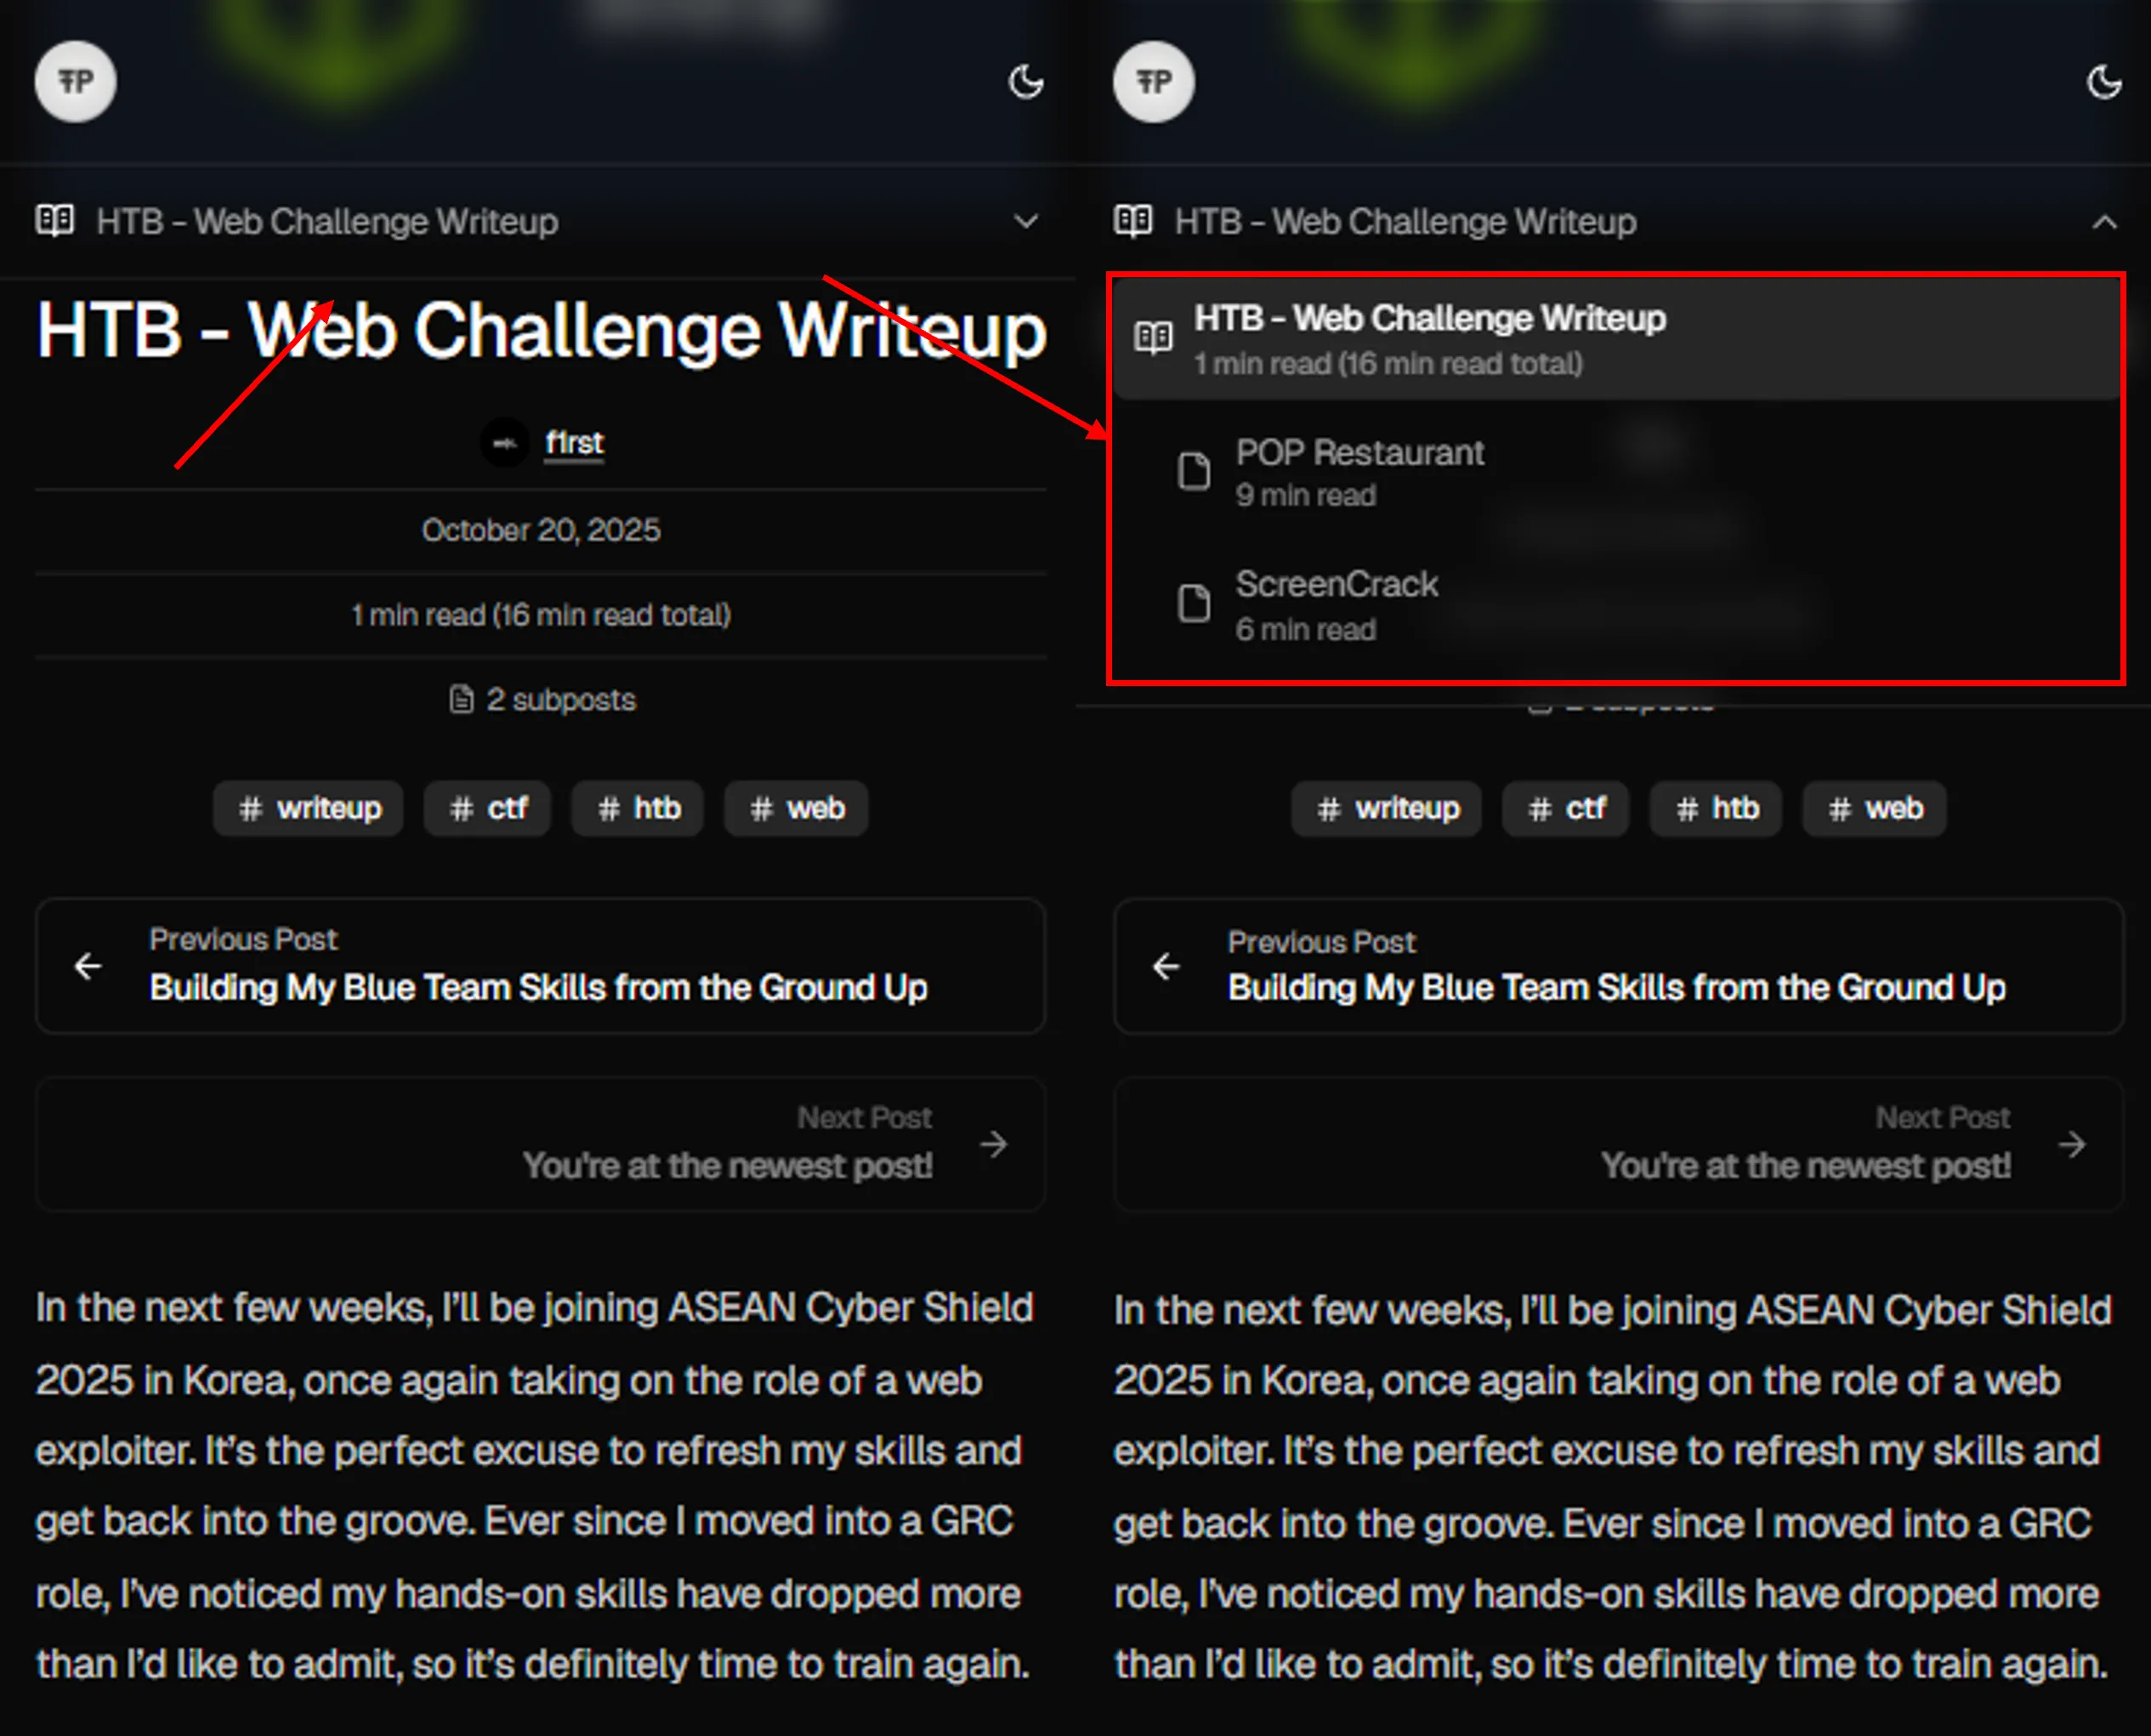
You can check out the sub-post on the side if you’re on desktop, or in the mobile navigation bar if you’re on your phone, for detailed writeups of each challenge.